Your risks, your controls, your audits. Connected, from the field to the Executive Committee.
Solvency II, DORA, AML/CFT: when they are tracked across spreadsheets, emails, and shared drives, follow-up becomes fragmented. A shared framework brings them together, so you can manage risk instead of being at its mercy.
Every risk, control, and obligation can be tied to the same framework. No more conflicting versions across departments.
Every team contributes to the same risk map. Weak signals become easier to spot, before they turn into problems.
From the field to the Executive Committee, data is consolidated, up to date, and shared. Everyone talks about the same risk, at the same time.
Every control, every action, and every incident is tracked in one place. Evidence is available when you need to present it, whether during an audit or a control review.
One shared framework, from the field to the Executive Committee.
Each module stays autonomous, but all share the same foundation. An incident updates the risk map. A control informs the audit. Data flows without re-keying. First line, second line, internal audit: three roles, one shared source of information.
From mid-sized companies to large corporations. They manage their risks with Delta RM.
Manage your risks, your controls, and your audits. In a single platform.
Built with risk professionals, for daily use. Each function keeps its specific requirements while sharing a common framework.
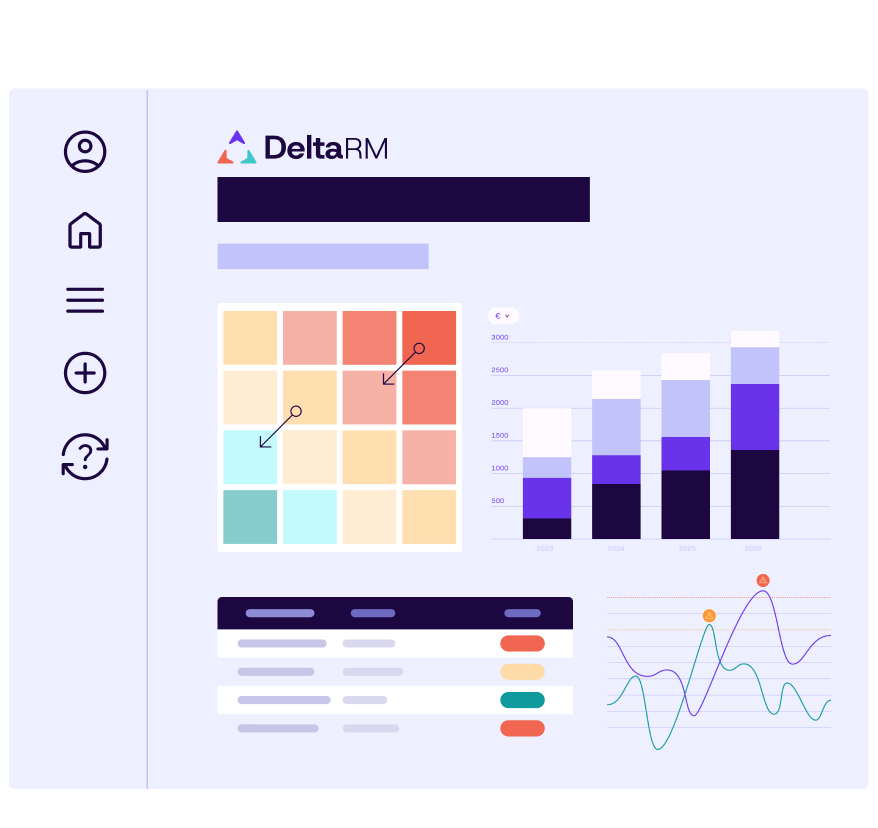
From risk mapping to steering, in a single tool.
From risk mapping to board reporting, everything rests on the same framework. Your teams contribute, control is demonstrated by facts, leadership decides with full visibility.
Visualize all your risks on a continuously updated criticality matrix. Filter by entity, process, risk category, or residual exposure level. Export in one click for your Executive Committee.
Formalize each control: define the objective, design it, set the scope, plan the frequency, and link it to its risks, processes, and regulatory requirements. One shared framework for the whole organization.
Plan your campaigns and choose your method: self-assessment, desk review, control checkpoints, testing, or sampling, with or without management sign-off. Each assessor attaches evidence directly to the assessment. Completion and compliance rates are tracked in real time.
Build your annual plan based on your risk mapping, control results, and recurring incidents. Each audit engagement is justified and validated.
Delta RM links each reported incident to the correct risk in your risk map. A net risk level is proposed in real-time, with no manual processing.
Upload your supporting documents: the AI agent analyzes their completeness and consistency, then scores each control. It identifies missing documents, detects inconsistencies across files, and generates a compliance report ready to share. You make the final scoring decision.
How we structure your GRC program.
In 3 steps.
Expert Scoping
We challenge the brief: we help you define the scope, assessment criteria, and taxonomies before we configure the platform. We know risk management from the inside.
Collaborative Rollout
We bring your teams on board: from scoping and configuration to training and go-live, we're there at every step. We stay with you until your teams have fully adopted the platform.
Continuous Monitoring
Your GRC program evolves over time: we help you refine it, enrich your data, and demonstrate the value of GRC to the Executive Committee.
Start with one module.
Activate the others at your own pace.
That's collective GRC.
An incident linked to its risk. A control linked to its evidence. An audit informed by both.
Everything is connected.
Policies, claims, insurable value collection, and loss ratio, linked to your risks. Report a claim directly from an incident, without re-entering data.
Prioritize your engagements in the most critical risk areas. Each audit updates your risk profile and closes the loop between exposure and control.
Plan your site visits and track your KRIs, from site to group. Document your risk prevention activities to strengthen your insurance submission.
Formalize your first- and second-line controls from your mapped risks. Measure the gap between gross and net risk.
They transformed their insurance management with Delta RM.
Insurers and mutual insurers whose risk, control, and audit teams have replaced scattered files with a structured, auditable, and shared GRC framework.

Frequently asked questions from risk teams in the insurance sector
The questions risk, control, and audit teams ask before choosing their GRC software.
SIGR (the French term for a risk management information system), GRC (Governance, Risk & Compliance), eGRC, and IRM are closely related terms for the same family of platforms, which centralize risks, controls, compliance, and audit. For your insurance programs, Delta RM also acts as an RMIS. For an insurer or a mutual insurer, it brings risk mapping, internal control, audit, and incidents together on one platform.
By linking internal control and audit to a shared risk framework: control campaigns (first and second line), audit engagements, incidents, and action plans are all tied to it. All teams work from that framework, structured around your reference standards (COSO for control, IIA Standards for audit), and reporting is consolidated without re-keying.
Delta RM is framework-agnostic: its configurable structure can be adapted to ISO 31000, COSO, Solvency II, DORA, or NIS2. In practice, you link your risks, controls, action plans, and evidence to your applicable requirements, starting with Solvency II. The platform is not meant to "make you compliant": it makes work, controls, and evidence easier to trace, without replacing the insurer's own responsibility.
Yes. Each entity manages its own scope, with group-level consolidation. The hierarchy goes up to 8 levels and access rights are granular: the group Risk Manager sees a cross-entity consolidation, while a subsidiary sees only its own scope.
No. Delta RM comes with unlimited users. You pay for the platform, not for each employee. It's a deliberate choice: collective GRC cannot be held back by per-user billing.
Yes, through the Insurance Management module: policies, claims, insurable value collection, loss ratio, and coverage analysis, connected to the risk and control base.
Yes. Data is hosted in France on Scaleway's European cloud infrastructure. The Delta RM platform is ISO/IEC 27001 certified and its hosting is SecNumCloud-qualified. Delta RM is an independent software vendor.
Is a feature missing from your system?
Our roadmap is built with you. You express a need. If it's shared, it becomes a product priority.