Internal Audit:
plan, execute, and monitor your engagements, from risk to recommendation.
No more audit plans in files. No more recommendations in emails. Delta RM structures your internal audit engagements, links each one to your actual risks, and gives your Executive Committee the visibility it needs.
From isolated engagements to a managed audit framework.
Internal audit is often seen as a burden. Delta RM transforms it into a driver for visible, measurable progress, directly linked to your actual risks.
Your engagements are prioritized based on the most exposed risk areas in your mapping. Every audit choice is justified, documented, and validated. You audit where it truly matters.
Each engagement is managed without switching tools, from planning to findings, recommendations, and action plans. Every step is tracked, timestamped, and accessible to your auditors and stakeholders.
Every recommendation becomes an action plan with an assigned owner and deadline. Progress is tracked automatically. No more recommendations lost in an email.
From mid-sized companies to large corporations. They manage their internal audits with Delta RM.


Everything you need to manage internal audits rigorously and without administrative overload.
Designed to help auditors spend more time auditing and less time managing files.
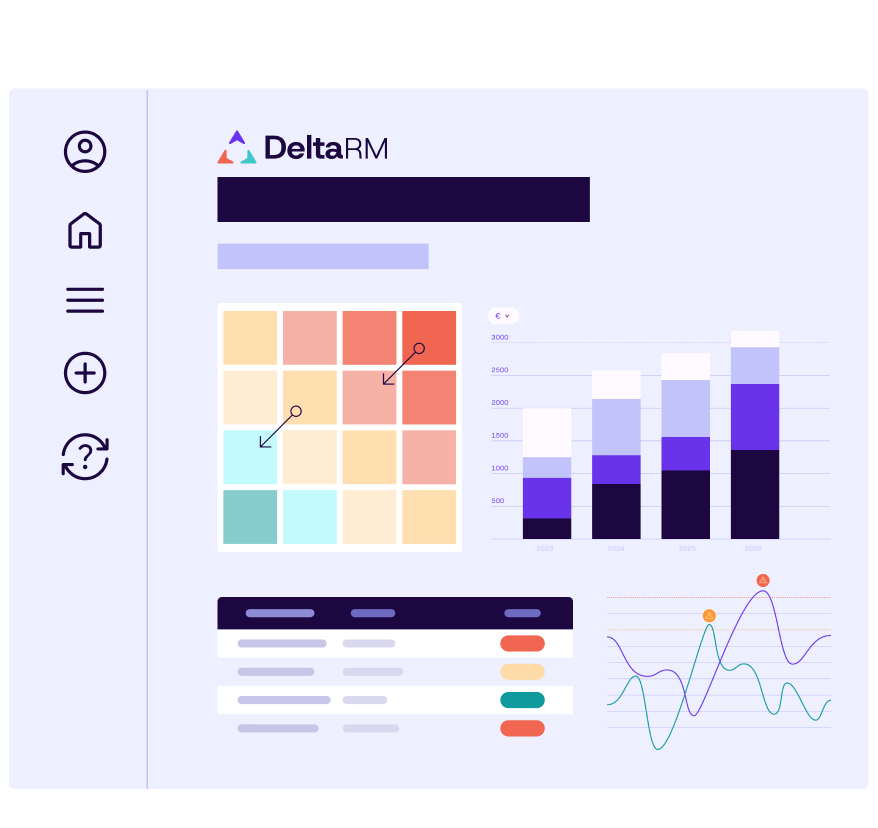
From planning to completion: everything is tracked, everything is monitored.
Designed in compliance with IIA standards. For audit professionals managing audit plans and complex engagements.
Build your annual plan based on your risk mapping, control results, and recurring incidents. Each audit engagement is justified and validated.
Manage every project from start to finish: scope, work plan, findings, recommendations, and reporting. Keep all your documentation in one place, accessible to all stakeholders.
Each recommendation generates an action plan with a designated owner and deadline. Automated reminders are sent for overdue tasks. Delta RM calculates your completion rate by engagement, entity, and owner.
Your auditees contribute directly to Delta RM: documents, findings, and action plans. No training required. From day one.
Generate your activity reports, track recommendations, and summarize covered risks. Your executives get a clear overview, with no need to reformat anything.
Upload your audit engagement evidence: the AI agent analyzes it for completeness and consistency, then automatically evaluates whether each finding is sufficiently supported. It identifies missing documents, detects inconsistencies across files, and generates a structured audit report, ready to be shared with auditees and the Audit Committee.
How we structure your internal audit.
In 3 steps.
Expert Scoping
We analyze your audit methodology, charter, and existing plan. We then structure them within Delta RM according to your standards, without having to start from scratch.
Collaborative Rollout
We configure the platform and train your auditors. Your first operational engagement will be ready in under two weeks, and your audit team will be fully autonomous from day one.
Continuous Monitoring
We help you implement key performance indicators to optimize your audit plans and demonstrate the value of internal audit to your governance team.
Start with one module.
Activate the others at your own pace.
That's collective GRC.
A high risk guides an audit engagement. An insufficient control triggers an audit. A recurring incident reveals an area to investigate. Everything is connected.
Prioritize your engagements in the most critical risk areas. Each audit helps update the risk map.
Prioritize your audits in areas of insufficient control. Your control results automatically feed into your audit plan.
Identify priority areas for audit based on recurring incidents. Connect operations and governance to strengthen the relevance of your audit plans.
Your visit reports inform your audit engagements. The third line relies on documented field evidence.
They transformed their internal audit with Delta RM.
Audit teams that replaced their shared files with structured, traceable engagements recognized by their Audit Committee.

SAVENCIA case study: a fun and interactive tool
The SAVENCIA project team shares their insights with you; the risk team has adopted our tool to consolidate a comprehensive risk map based on assessments from their entities.
Industrial (international food group) Independent family-owned group, operating in 120 countries (dairy products, chocolate, charcuterie, and seafood)
SAVENCIA case study: a fun and interactive tool
The SAVENCIA project team shares their insights with you; the risk team has adopted our tool to consolidate a comprehensive risk map based on assessments from their entities.
Industrial (international food group) Independent family-owned group, operating in 120 countries (dairy products, chocolate, charcuterie, and seafood)
Risk intelligence, by those who practice it.
The latest analyses from our experts to better manage your risks.


Frequently asked questions about internal audit
Questions asked by audit managers, CFOs, and audit committee members before choosing their tool.
Delta RM connects your audit plan to risk mapping, your control results, and your recurring incidents. You build your plan on data, not habits.
Yes, via structured Excel or CSV import. Our team supports the migration process in 3 steps: analysis of your existing audit plan structure (engagements, scopes, methodology), mapping to the Delta RM model (nomenclature and repository alignment), and controlled import with user validation. No loss of information: historical engagements, findings, recommendations, action plans, and their statuses are operational from the first use. The typical import time is less than 5 days for a standard annual audit plan.
Delta RM automatically calculates your recommendation implementation rate by engagement, entity, and manager. This dashboard is directly shareable with your Audit Committee.
Yes. The module complies with the IIA Global Internal Audit Standards 2024 and IFACI best practices for the French-speaking context. Specifically: audit engagements are structured according to a sequence of planning, execution, communication, and follow-up; findings and recommendations are traceable; and work programs are documented in compliance with external quality review requirements. Our teams include auditors who designed these workflows.
Yes. Delta RM is designed to scale with your team's size. A team of 1 to 3 auditors benefits just as much as a department of 20 from structuring engagements, tracking recommendations, and preparing for Audit Committees.
Internal control is a continuous process of evaluating control mechanisms. Internal audit is a periodic, independent evaluation engagement. In Delta RM, the two are connected: your control results feed into your audit plan.
Less than 2 weeks for an audit team to be operational with an existing methodology. 4 to 6 weeks if we formalize your methodology within the platform. The first operational engagement can begin immediately after deployment.
Delta RM separates audit workflows from control and risk management workflows. Internal audit has read-only access to data from other modules. Your stakeholders (Audit Committee, regulators) can view governance and access rights to demonstrate independence.
Yes. All your working papers, audit programs, findings, recommendations, and final reports are hosted in France (Île-de-France region), on ISO 27001 certified and SecNumCloud qualified servers, outside of any US cloud infrastructure. Your internal auditors, auditees, and Audit Committee members access a sovereign environment. This is a strong requirement for audit functions in banks, mutuals, provident institutions, and essential service operators.
Yes. The Internal Audit module can be configured to align with key professional standards: ISO 19011 (guidelines for auditing management systems), IIA Global Internal Audit Standards 2024 (the Performance Standards and Attribute Standards that replaced the IPPF in January 2025), and the IFACI framework for the French-speaking context. The structuring of audit engagements, the traceability of findings, and the documentation of work programs comply with the IIA's quality review (peer review) requirements.
Your internal audit charter, approved by the Audit Committee, is integrated into Delta RM as the foundational document for the framework. Roles, responsibilities, scope of activity, access rights, and independence rules are configurable according to your charter. Any governance change (charter redesign, scope changes, approval by the Audit Committee) is tracked and auditable, including for an external quality review (IIA peer review).
Is a feature missing from your system?
Our roadmap is built with you. You express a need. If it's shared, it becomes a product priority.